


The enterprise MCP gateway that governs the action, not just the connection.
Willow gives every AI agent a real identity, only the tools its task needs, runtime guardrails, and an audit trail tied to a human. Claude, Cursor, ChatGPT, Codex and Copilot connect through one governed endpoint.





Security won't approve. Employees won't wait. Nobody can see what's running.
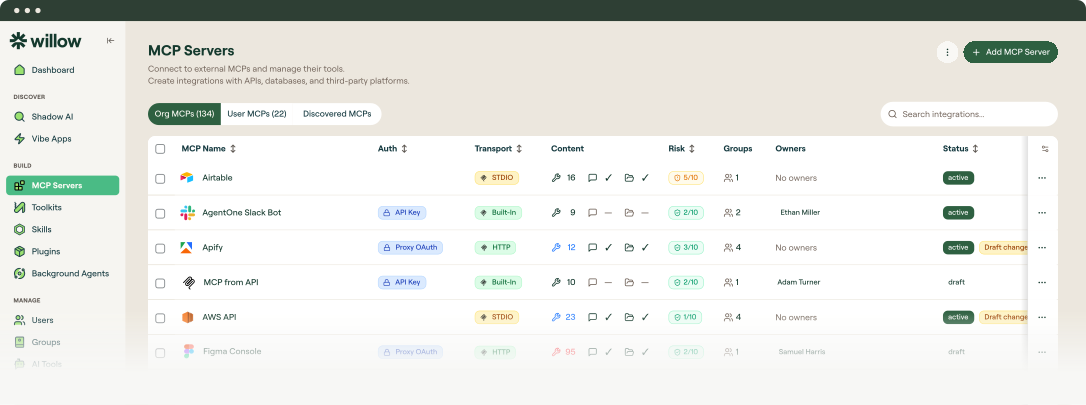
An MCP gateway sits between your agents and their tools. Most just route traffic. Willow governs what each agent can see, do and touch.
No inventory
How many MCP servers are connected to your org right now? Nobody knows.
Shadow MCP
Installed from a README. Approved by no one.
Over-permissioned
Agents inherit the full access of whoever pasted the key.
Ticket backlog
Every connection is a security review. So people go around it.
Six checks on every call. Then it's logged.
AI clients connect to a Willow MCP URL instead of the tool directly. Every request passes the same checks, in order, before anything touches your data.
Identify
A real identity from Okta, Entra ID, JumpCloud or Google. Agents and machine users get their own, tied to a human owner.
Scope
Group membership decides which servers and tools this user and agent can see. Nothing more.
Enforce policy
Only allowed tools and actions run. Conditions check live context, like channel, repo or data label. If a check fails, the call is blocked by default.
Inspect
Guards scan every request for prompt injection, secrets and PII before it leaves Willow.
Broker credentials
Willow proxies the call with credentials from an encrypted vault. Nothing long-lived in a config file.
Clean the response
Response guards mask PII and credentials before anything reaches the model.

Most MCP gateways route the call. Willow governs what happens inside it.
A catalog, SSO and audit logs are table stakes. Here is what enterprise teams get on top.
Least privilege at runtime, not after the fact
Other gateways grant a bundle of tools and hope guardrails catch misuse. Willow's Dynamic MCP endpoint surfaces only the tools each conversation needs. The agent can't misuse a tool it never sees.
Guardrails that hope to catch mistakes vs. tools that can't make them.
Context-aware conditions
Allow posting in eng-*, block exec-*. Allow Drive reads, block anything labeled Confidential. If the check fails, the call is blocked by default.
Action-level control
Govern which Jira projects, Snowflake schemas and GitHub repos an agent touches, not just whether it connects.
Risk score per server
0 to 10, weighted by auth method, write and delete tools, and active guards.
Rate limits
Set per user, per group and per server.
Lower token spend as a side effect.
One customer cut token use on certain tool operations by as much as 95%. Fewer tools in context means less for the model to read.
Find shadow MCP servers before they find your data
Most gateways only see traffic routed through them. Willow looks at what's actually installed, then brings what's worth keeping under governance.
Scan agent, pushed through MDM
Jamf, Intune, JumpCloud, Mosyle or GPO, on macOS and Windows. Finds MCP servers in Cursor, Claude Desktop, VS Code and Windsurf, plus skills, CLAUDE.md and AGENTS.md files, and AI coding tools.
Willow Guard browser extension
Covers ChatGPT, claude.ai, Gemini and M365 Copilot.
Allow, warn or block
By user, group or device.
“Willow gave us a single platform to govern and secure our developers' local machines, especially around exposure to MCP servers and external skills.”
Runtime guardrails built for MCP security
DLP and IAM were built for users and files, not agents and prompts. Willow enforces policy inline, on every request and every response.
Runtime guards for prompt injection, secrets and PII, plus Regex, JSONata, LLM-judge and custom-function checks.
Build-time guards stop toolkits, skills and plugins with hardcoded credentials from being published.
Guard hooks inside Claude Code, Cursor and Codex, delivered by MDM or the marketplace.
Bring your own engine: Prompt Security, Alice, or a custom webhook.
SSO, SCIM and RBAC for MCP access control
No new identity model. Your IdP groups become agent permissions on day one.
SCIM v2 user and group provisioning.
JWT passthrough so internal MCP servers see the real user.
Agent auth without static secrets: OAuth 2.0, token exchange, impersonation, and scoped machine users for background agents.
Vault with AES-256-GCM. Keys in AWS KMS, or your own on-prem. Every secret operation audited.
MCP audit logging your SIEM can actually use
A dashboard shows activity. An audit trail shows which agent, on whose behalf, touched which data, under which policy.

OTLP intake
From Claude Code, Codex, Cursor and Cowork.
Claude Compliance sync
Flags secrets and PII in claude.ai chats.
Adoption analytics
Weekly active users, top tools, blocked vs. passed actions. Prove AI is working.
Connect anything. Wrap any API as MCP.
Built-in connectors, the MCP Registry, and your own servers, all governed the same way. Reach without a ceiling.





Self-service for employees. Governance as code for platform teams.
IT goes from bottleneck to enabler. Weeks of tickets become minutes to a governed connection.
Connect Panel and plugin marketplace. Employees one-click approved tools into Cursor, Claude Code, Copilot CLI and Codex.
GitHub and Bitbucket sync. MCP servers, toolkits, skills and plugins live in your repo and sync both ways.
Your admin turned this server off. It won't show up in the Connect Panel, and agents can't reach it from any client.
No ticket, no back-and-forth. We'll notify you as soon as your admin approves it, and it connects automatically.
Live in Cursor, Claude Code, Copilot CLI and Codex, scoped to your groups and logged to your SIEM.
Self-hosted, hybrid or air-gapped MCP gateway
Deploy where your compliance lives. Helm on EKS, GKE, AKS, OpenShift or any conformant Kubernetes 1.23+.
Managed by Willow. US and EU regions.
Runtime in your Kubernetes. Tool calls never leave your network.
Every component in your cluster. Air-gapped, no call-home.
MCP gateway vs. API gateway vs. Willow
MCP gateway vs. API gateway
Willow vs. a routing-only MCP gateway
"We are six to ten months ahead of most companies in AI adoption. More code to production, fewer incidents, real outcomes. Willow is what made it possible to move that fast without slowing down our security posture."
Wix runs about 600 governed tools and MCPs through Willow, across HR, legal, finance, design and R&D. An office manager who used to walk hundreds of meeting rooms every month now frees the empty ones with one prompt.

Your agents are already in the wild.
Give them a Basecamp. Go from AI chaos to AI work, in minutes.
