


Chat and Cowork Are Merging: What Enterprises Need to Know
Anthropic is merging Claude's chat and Cowork into one experience. Users no longer pick between a chat window and a separate desktop agent. The same conversation can now run code, work with files and keep long tasks going in the cloud. The move puts Claude head to head with OpenAI's ChatGPT Work and Google's Gemini Enterprise.
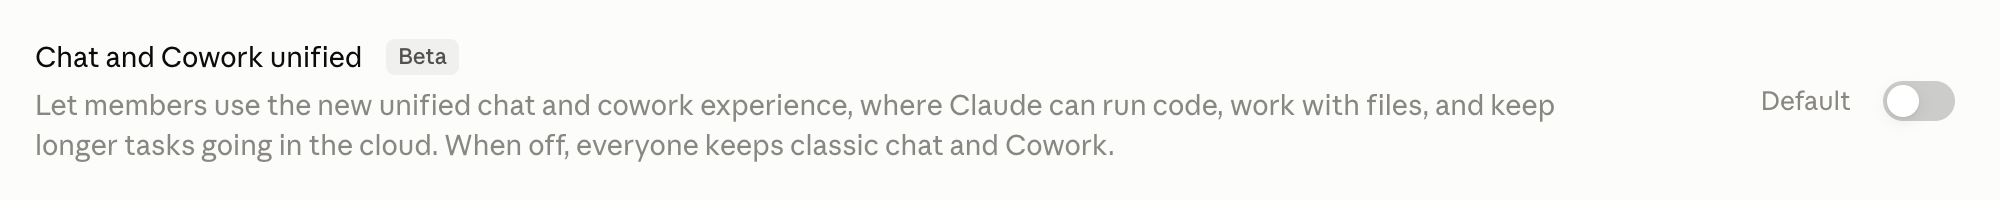
For users, that removes a choice. For security teams, it changes the default: any chat can turn into an agent that takes actions. In the admin console the switch is called Chat and Cowork unified. It's in beta and off by default, so you have time to set guardrails before your people get it.
What's changing
Unified Claude is a chat that turns itself into an agent when a task calls for it. Anthropic announced it on September 16, 2026. Pro and Max accounts are moved over automatically and can't switch back. Team and Free plans follow soon. Enterprise gets it as an opt-in beta, with at least 30 days' notice before anything changes.
- One conversation, two modes. Every conversation starts as a regular chat. When a task needs to run code or work through files, Anthropic's service moves it into an isolated cloud virtual machine (VM), and back again when it's done. The service makes that call, not the user or the model.
- Context moves with it. When a chat moves into the VM, its history, attached files, project files, saved preferences and skills are copied there.
- Work keeps going without the laptop. Long and scheduled tasks keep running in the cloud with the lid closed. Users pick them up again from the browser, the desktop app or their phone.
- The laptop can still join in. A user can link their computer through the desktop app. Claude can then use the folders they grant, local MCP servers, the screen and the browser. That works even when the session was started from a phone.
- Admins decide who gets it. The Chat and Cowork unified setting (beta) is off by default and can be granted by role. It needs Chat and Cloud code execution turned on, but not Cowork. It isn't yet available to organizations that use customer-managed keys (CMEK), zero data retention (ZDR) or HIPAA configurations.
Chat vs. Cowork: what's actually different
Chat was a conversation you steered. Cowork was a task you handed off. Unified Claude decides which one each request needs, and that choice changes where the work runs and what it can touch.
The old modes didn't share context. Chat only knew its own conversation, and Cowork sessions reset when they ended. Memory has been shared since August 2026, and unified Claude now carries chat memory into its tasks.
What to watch
The merge widens what one conversation can reach, and several controls you rely on today don't cover the new paths.
Each path has its own setting, and the checklist below covers every one.
- Any chat can become an agent and keep working alone. The service moves a conversation into a cloud VM on its own, and shell and file work inside it don't ask for approval. Long and scheduled tasks then run with nobody watching.
- Your network controls go blind. Cloud sessions leave from Anthropic's infrastructure, so your proxy, VPN, firewall and IP allowlists never see the traffic. Egress settings don't cover web search, web fetch or MCP connectors, and customers can't access Anthropic's egress logs.
- A phone can reach a laptop. With Remote control on, a session started on the web or a phone can use files, tools and apps on the member's computer. Require trusted devices is off by default. Remote control and scheduled tasks can only be set org-wide, not per role.
- Local MCP servers are a side door. MCP servers and desktop extensions installed on a laptop never show up in the admin console. Cloud sessions can still reach them through the desktop app, and only an MDM device policy turns them off.
- The browser acts as the user. The built-in browser and Claude in Chrome use the member's logged-in sessions to read pages, fill forms and drive web apps. The built-in browser has been on by default for Enterprise since September 10, 2026.
- Approval modes can take the human out. "Automatically approve" lets a classifier decide on connector calls. "Skip all approvals" covers scheduled tasks and the built-in browser. "Always allow" pre-approves write tools, and Anthropic calls the remaining prompt-injection risk "non-zero."
- Data lands in more places. Each agentic chat creates a second copy in its cloud session. Standalone cloud sessions, scheduled runs and memory (during the beta) aren't covered by custom retention. Data is stored in US regions only.
- Visibility has gaps. EDR can't see inside the local or cloud VM. The Compliance API covers unified conversations, but for local sessions it shows what Claude was asked and answered, not what happened on the computer.
- Personal accounts already have it. Pro and Max users were moved over automatically, and since October 6 their new tasks run in the cloud by default. An employee who connects work systems to a personal account is running a cloud agent outside all of your controls.
Admin checklist before you turn it on
Set these before the first user gets unified Claude. Most live under Organization settings in the admin console. Device keys go out through your MDM (Jamf, Intune or Group Policy).
Write down every deviation from this baseline and the reason for it.
Why Willow keeps Cowork safe
Anthropic's console decides what Claude may do, with org-wide switches. It can't see what's installed on a laptop, inspect what a tool call carries, or give you a record you control. Willow closes those gaps at four points: the model, the connectors, the laptop and the browser.
Each layer works on its own, and all four write to the same audit trail.
1. Every prompt and tool result goes straight to the model
Willow Inference Hooks sit in front of the model on every Claude Enterprise surface: claude.ai, Cowork and Claude Code.
- One organization-level setting in claude.ai. Nothing to install on laptops.
- Before a prompt, or a tool result Claude is about to read, reaches the model, Anthropic sends it to Willow. Willow returns allow or deny, and a denied request never reaches the model.
- Guards check for prompt injection, secrets and PII, plus your own regex, JSONata, LLM-judge or custom-function rules. Every denial is logged in Willow and in Claude's activity feed.
2. Approvals users can switch off
Claude's approval modes are a user choice. Willow's approvals are policy.
- Add Willow to Claude as a single connector; it's listed in Claude's Connectors Directory. Every tool call then passes Willow's MCP gateway.
- Permissions are set per action, not per app. Reading code, opening a branch, merging a PR and deleting a repo are separate decisions.
- Conditions check live context, such as "post in eng-* channels, never exec-*" or "no Drive files labeled Confidential." A failed check is blocked by default.
- Critical actions go to a person in Slack with full context, one click to approve or deny. That holds even when the user runs Claude in Automatically approve.
3. Agents get more access than the task needs
- Identity comes from Okta, Entra ID, JumpCloud or Google. Your IdP groups decide which servers and tools each person's Claude can see.
- Dynamic MCP shows each conversation only the tools it needs. An agent can't misuse a tool it never sees.
- Credentials come from an encrypted vault at call time, so no long-lived tokens sit in config files. Each server gets a 0–10 risk score, and rate limits apply per user, group and server.
4. Sensitive data flows into the model
- Guards scan every request and every response. PII and credentials in tool responses are masked before Claude ever reads them.
- Claude Compliance Sync pulls your Claude chats from the Compliance API every hour. It flags messages with secrets or PII and shows them next to your tool-call logs.
5. Laptops and personal accounts the console never sees
- The Willow Scan Agent, pushed through Jamf, Intune, JumpCloud, Mosyle or Group Policy, finds MCP servers in Claude Desktop, Claude Code, Cursor, VS Code and over a dozen other AI clients. It also finds skills, plugins, CLAUDE.md files and installed agents.
- It shows which inference provider each Claude Desktop install sends requests to, so a gateway like OpenRouter or Bedrock can't hide.
- Policy rules allow, warn on or block what it finds, per user, group, device or agent. Before you publish one, Willow replays it over the last 30 days of real traffic and shows who it would have blocked.
- The Willow Guard browser extension covers claude.ai, ChatGPT, Gemini and M365 Copilot, including personal accounts that network blocks miss.
- A Willow-managed plugin marketplace syncs into Claude's organization plugin library. Build-time guards stop skills and plugins with hardcoded credentials from being published.
6. The browser acts as the user
Willow for Chrome is the policy layer for Claude in Chrome.
- Access is scoped per app, per URL and per action: read, edit, send or block.
- Before Claude sends, submits, posts, pays, deletes or uploads, Willow freezes the action and shows the full payload for approval.
- PII and secrets are redacted in the browser before the model reads them. The extension is free and open source.
7. No record you own
- Every tool call is logged with the person behind it, the agent and the policy that allowed or blocked it. Logs stream to Splunk, Grafana, Loki, CrowdStrike or any webhook.
- Willow also takes in OpenTelemetry from Cowork and Claude Code, so chats, agent activity and tool calls sit on one timeline.
The merge makes Claude one more agent acting on your systems, next to Cursor, ChatGPT, Codex and Copilot. Willow gives all of them one identity model, one policy and one audit trail. That's how you turn unified Claude on for everyone, not just a pilot group. Book a demo.
Sources
- Claude Cowork and chat are now one Claude, Anthropic, September 16, 2026
- Set up and manage the new unified Claude experience for your Enterprise organization, Claude Help Center
- Choosing between Claude Cowork or Chat, Claude Academy
- Unified Claude Security Best Practices, v1.3.1, Anthropic Trust Center, September 30, 2026
- Willow MCP Gateway, Willow
- Inference Hooks, Willow docs
- What the Scan Agent does, Willow docs
- Policy Rules, Willow docs
- Claude Compliance Sync, Willow docs
- Willow for Chrome, Willow
- Shadow AI, Willow
- Governance and Compliance, Willow
Background Agents in the Enterprise
Most teams can spin up an agent. Few can deploy one their security team signs off on. Here's the framework that does both.
FAQS
Everything you need to get your Basecamp running.


Your agents are already in the wild.
Give them a Basecamp. Go from AI chaos to AI work, in minutes.
