
Willow finds supported employee AI before registration and also governs OAuth, per-user credentials, individual tool calls, remote MCP servers, and browser activity. Arcade packages OAuth, tool execution, and policy hooks into a developer-oriented actions runtime.
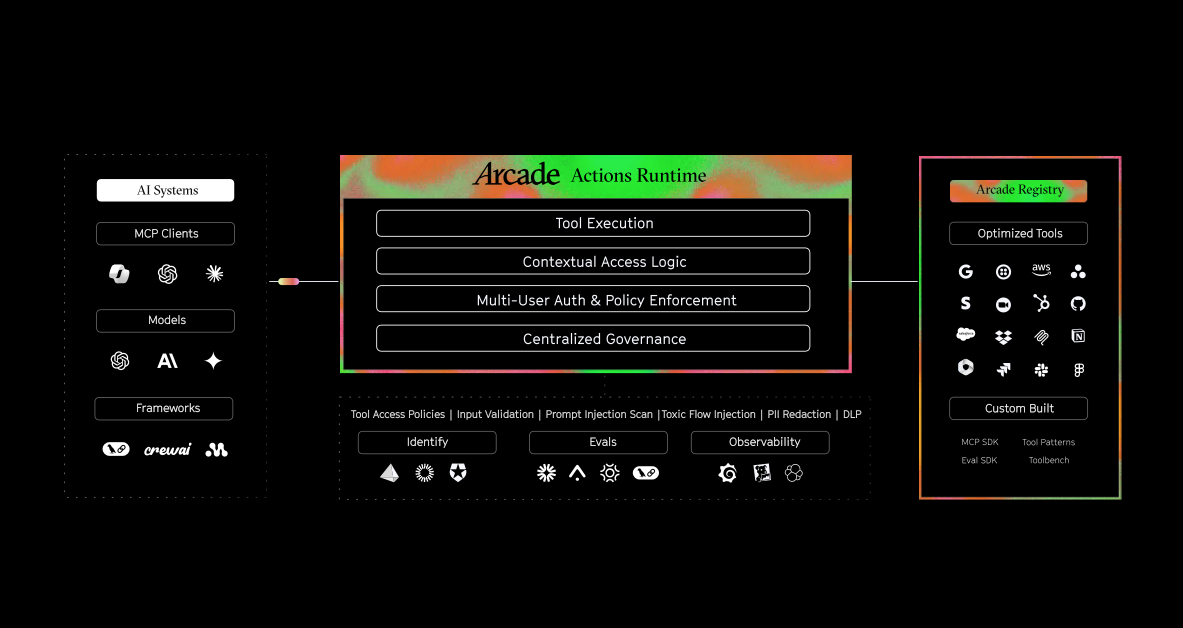
Both products support OAuth, per-user credentials, MCP gateways, tool policy, audit, and private deployment. Willow adds employee-device and browser discovery. Arcade offers a developer-focused actions runtime and hook model.

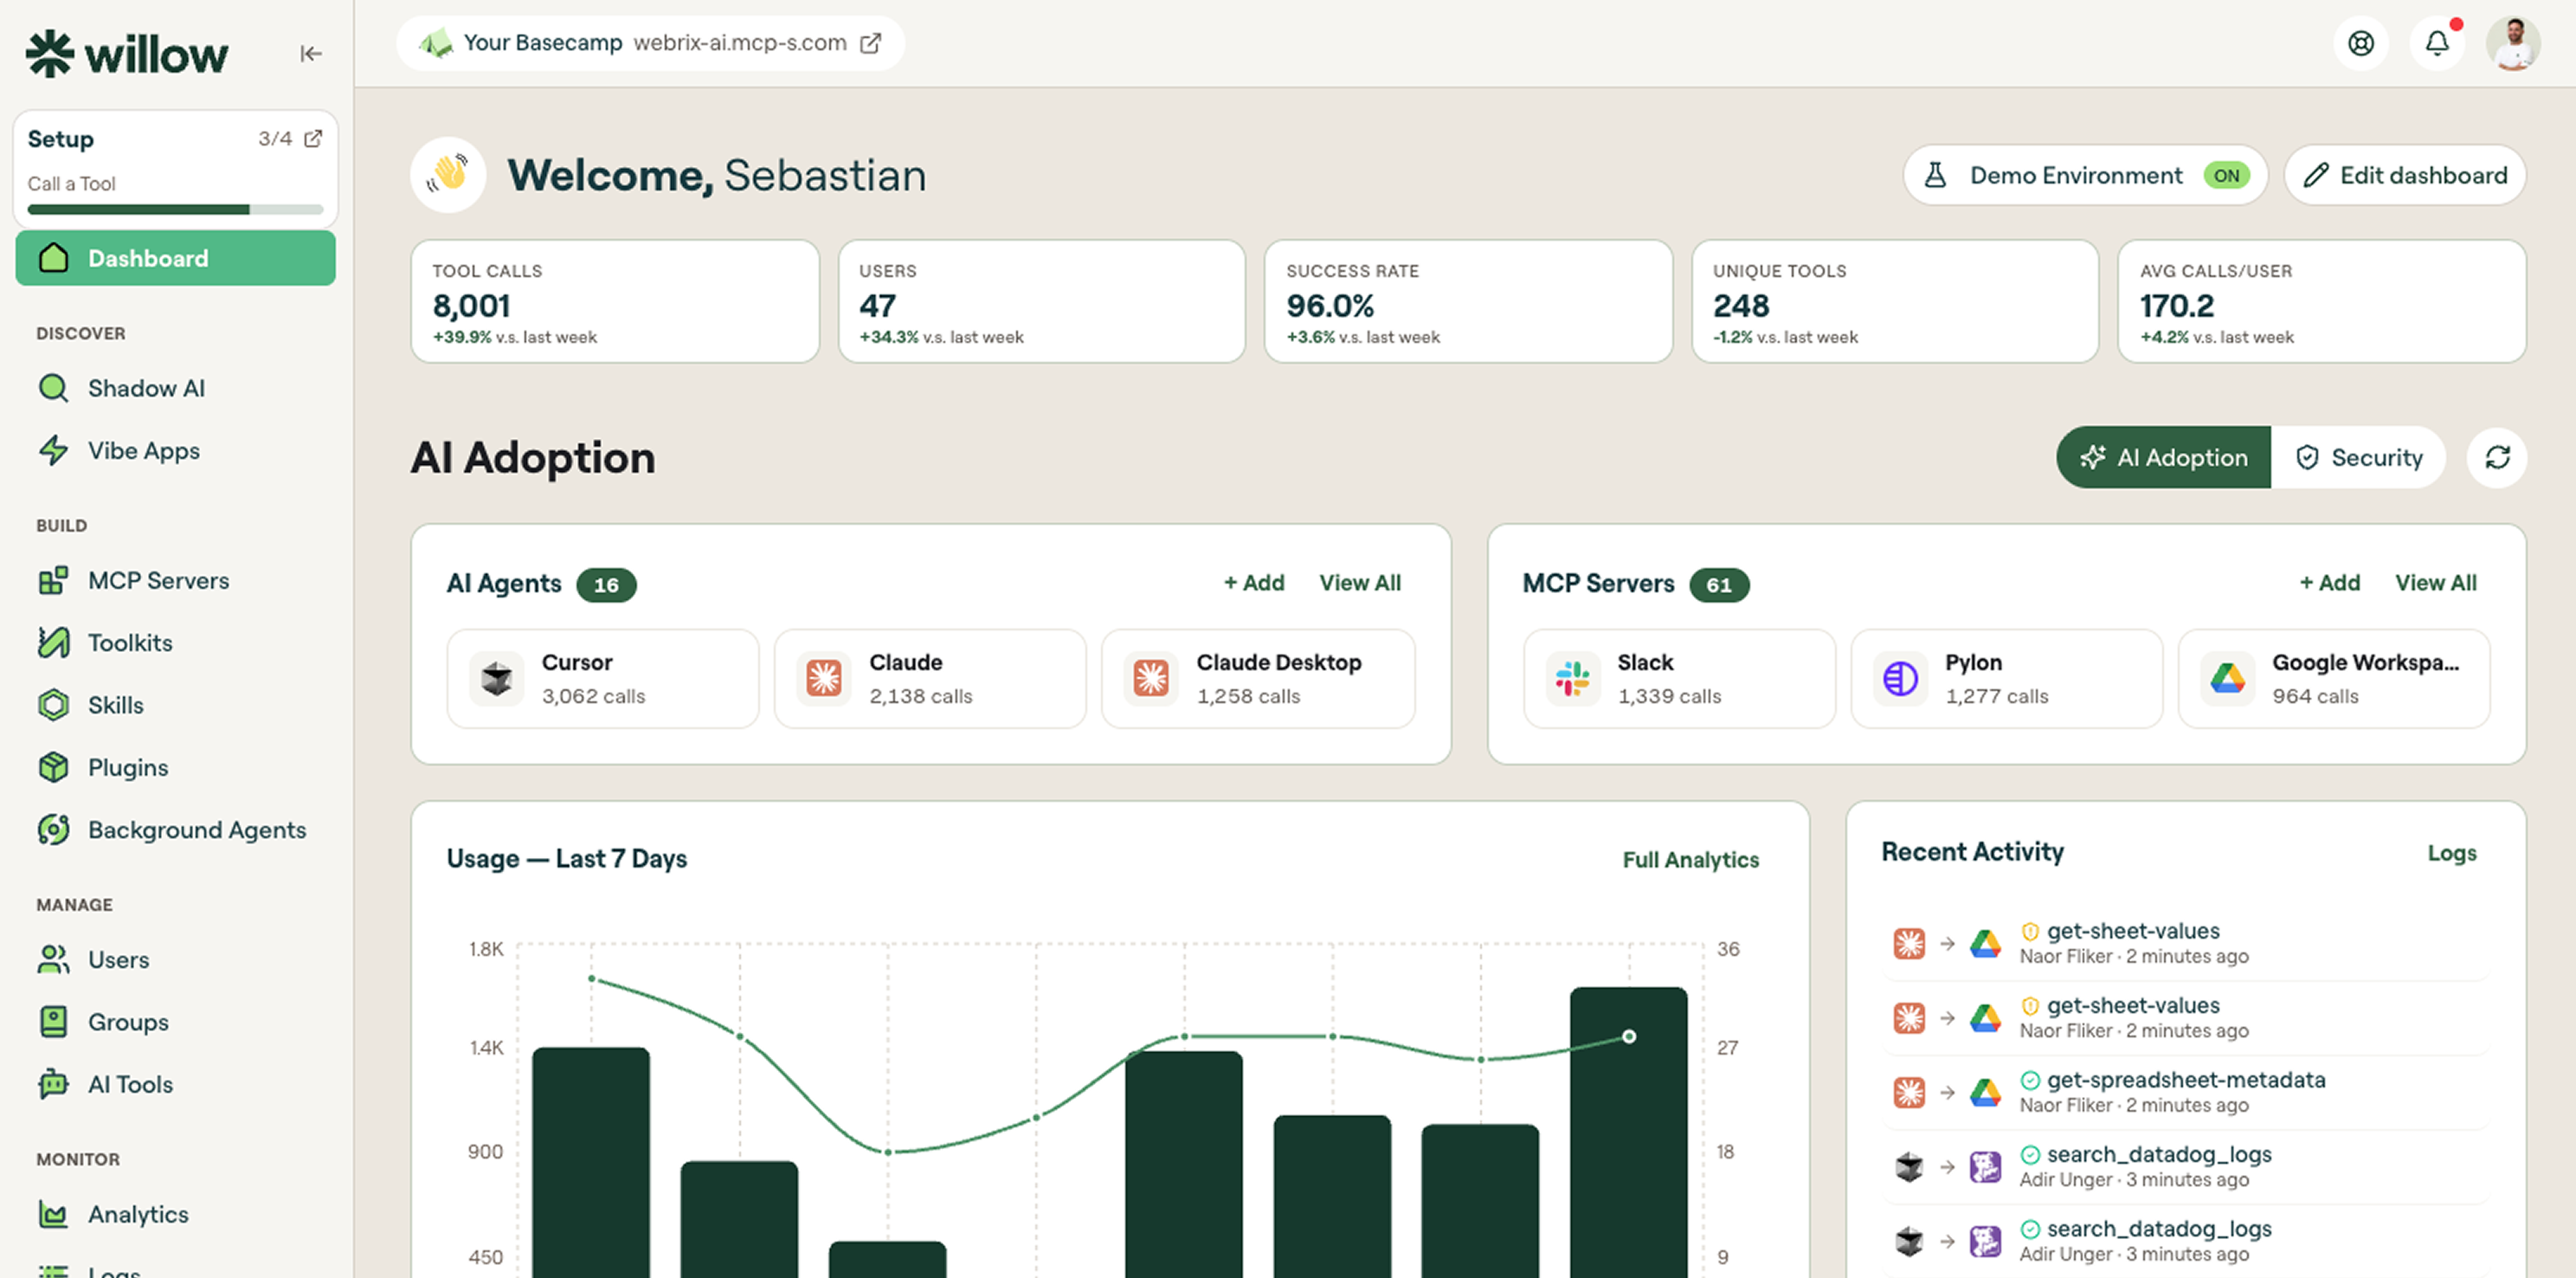
Willow finds supported AI tools and files on managed devices. It also governs supported browser AI, machine users, and background agents.

Arcade combines OAuth, tool execution, and policy hooks in an SDK-oriented runtime for agent developers.
We are six to ten months ahead of most companies in AI adoption. More code to production, fewer incidents, real outcomes. Willow is what made it possible to move that fast without slowing down our security posture.

weekly active users at Wix
governed tools and MCPs
governed tool calls every week

Willow finds supported AI use that employees configured locally or accessed in supported browsers, then gives IT and security one place for identities, policy, MCP access, and background agents. Arcade packages similar OAuth and tool-call controls into its own actions runtime and SDKs for agent developers.
Use Willow if you need managed employee AI discovery and governance, with per-user OAuth, tool-call policy, remote MCP access, and browser controls in the same platform. Use Arcade if your developers specifically prefer its actions SDK, Contextual Access hooks, or an Arcade-provided tool. If both requirements matter, test how identity, policy, and audit records will remain consistent across the two systems.
Common questions from teams comparing Willow with Arcade.
Give them a Basecamp. Go from AI chaos to AI work, in minutes.


